Defending Against
AI-Powered Threats
A Full-Day Hands-On Workshop for Cybersecurity Leaders. 3 masterclass modules + 9 real-world micro projects. Analyse real attack logs. Extract live IOCs. Leave with a control gap assessment and 9 earned badges.
The Problem: AI Has Changed the Attack Landscape
What Your Security Team Faces Today
- ·AI-generated phishing emails now achieve 57% click-through rates — nearly double traditional campaigns.
- ·LLM-written attacks bypass grammar and signature-based filters entirely.
- ·Deepfake audio is being used to impersonate CFOs and CISOs in live vishing attacks.
- ·Adversarial ML is poisoning UEBA baselines, hiding attacker behaviour in statistical noise.
- ·AI supply chain attacks compromise model weights before deployment — invisible to standard controls.
Most security programmes were built for 2019-era threats. The controls that exist today will not stop an AI-augmented attacker in 2025.
What This Workshop Changes
- ✓You will read and analyse real AI-threat logs — not slides about them.
- ✓You will extract live indicators of compromise from an active campaign dataset.
- ✓You will apply MITRE ATT&CK for Cloud to map your own detection gaps.
- ✓You will leave with a one-page control gap list specific to your environment.
- ✓You will earn 3 CPE credits recognised by ISC2, ISACA, and CompTIA.
Grounded in the NoowaPay Silent Phantom attack — AI-generated phishing, AWS credential theft, and a 6-day undetected breach of 1.5 GB of customer payment data.
Who This Is For
Open to all professionals with a basic understanding of cybersecurity and AI concepts — from practitioners to leaders.
Right Fit
- ✓CISOs, CIOs, VPs and Heads of Security
- ✓Security Architects and Principal Engineers
- ✓SOC Managers and Detection Engineering Leads
- ✓IT and Security professionals curious about AI threats
- ✓GRC and Compliance leaders with security oversight
- ✓Developers and Cloud Engineers working in security-adjacent roles
- ✓Anyone with basic cybersecurity knowledge and interest in AI
Prerequisite
A basic familiarity with cybersecurity concepts (e.g. what a SIEM is, what phishing means) and general awareness of AI. No hands-on lab experience required — curiosity about evidence is enough.
Not the Right Fit
- ·Complete beginners with no exposure to IT or security
- ·Sales or product teams seeking market intelligence only
The Three Modules
Each module: 20-min masterclass → 30-min guided lab → 10-min debrief. All three connect into a single attack narrative.
AI Threat Landscape
What AI has fundamentally changed about the threat landscape — why your current tools have a blind spot, and how to read the new evidence trail.
- ·Parse a real LLM audit log in JSONL format and count flagged injection events.
- ·Triage events by flag reason to find the most common attack pattern.
- ·Extract injection_succeeded events and identify the attacker account.
- ·Evaluate which guardrail control would have closed the detection gap.
- ·Debrief: each participant names one AI threat their org is not currently monitoring.
AI Phishing Detection
The attacker used an LLM to write a personalised phishing campaign with a 27% click rate. You analyse the SMTP log, extract IOCs, and close the authentication gap.
- ·Count delivered emails, click events, and credential submissions from a live SMTP log.
- ·Extract the sending domain from MAIL FROM headers using regex as an actionable IOC.
- ·Identify SPF, DKIM, and DMARC failures as indicators of AI-generated phishing.
- ·Calculate campaign effectiveness metrics and scope the breach response.
- ·Debrief: participants audit their own domain's DMARC record live.
LLM Prompt Injection
A contractor account ran a multi-session prompt injection against the NoowaPay AI assistant — and exfiltrated credentials. You reconstruct the attack from the audit trail.
- ·Identify the user account responsible for a successful LLM prompt injection.
- ·Extract session identifiers and calculate total token usage across targeted events.
- ·Decode a base64-encoded exfiltration payload to recover the leaked credentials.
- ·Write a detection rule that catches prompt injection patterns in LLM audit logs.
- ·Debrief: each participant identifies their highest-priority remediation action.
Hands-On Micro Projects
9 case-study labs — 3 per module — based on real 2024 breaches. Each takes 20–25 minutes and awards a badge on completion. Included in your 72-hour post-workshop lab access.
Module 1 — AI Threat Landscape
The Campaign That Broke Every Filter
AI-targeted phishing — 800 US accounting firms, 2024
The Attack That Looked Normal
Salt Typhoon UEBA bypass — US telecom carriers, 2023–24
Triage the AI Audit Log
WormGPT-assisted BEC — financial services, 2024
Module 2 — AI Phishing Detection
The $25M Deepfake Call
Arup Engineering BEC — February 2024
The AI Voice Clone Attack
Ferrari executive vishing — July 2024
Spot the AI Phish
IBM X-Force phishing research — 2024
Module 3 — LLM Prompt Injection
The Email That Rewrote Itself
EchoLeak CVE-2025-32711 — Microsoft 365 Copilot, May 2025
The Channel That Answered Too Much
Slack AI RAG poisoning — PromptArmor, August 2024
The Ticket That Approved Itself
ServiceNow Now Assist agent injection — 2024
Part of a Larger Story
These 3 modules are Arc 5 of the full AISA course
The NoowaPay Silent Phantom breach you investigate today starts in Chapter 1 of our 40-chapter AISA: AI SOC Analyst programme. The SSH brute-force, the phishing click, the AWS credential theft, the lateral movement to Azure -- all of it leads to the AI-powered techniques you see in this workshop.
Workshop Agenda
Full-day format · 09:00 – 18:00 · 9 hours including breaks · 6 CPE Credits
Morning — Masterclass Labs (3 hrs)
Afternoon — Micro Project Labs (4.5 hrs)
Three lab sessions, one per module. Each session runs 3 micro projects back-to-back with a short debrief. Students work at their own pace — facilitator circulates.
What You Get in the Lab
- ·Dedicated browser-based terminal session
- ·Pre-loaded NoowaPay CloudTrail + email gateway logs
- ·Structured lab question set with expected outputs
- ·72-hour post-workshop lab access for review
Technical Requirements
- ·Laptop or tablet with modern browser (Chrome / Firefox)
- ·Stable internet connection (minimum 5 Mbps)
- ·No VPN, extensions, or software installation required
- ·Mobile phones not recommended for lab work
Certification & CPE Credits
Certificate of Completion
CyBe Global — digitally signed, PDF issued same day
6 CPE Credits
ISC2 CISSP · CISM · CompTIA Security+ · CEH eligible
Continuing Education
Counts toward annual CPE maintenance for most certifications
CPE Credit Verification
CyBe Global is a recognised CPE provider. All participants receive a CPE completion letter on the day of the workshop, suitable for direct submission to your certifying body.
Covered bodies: ISC2 (CISSP, CCSP, CSSLP) · ISACA (CISM, CISA, CRISC) · CompTIA (Security+, CySA+, CASP+) · EC-Council (CEH, CHFI) · SANS GIAC
What Participants Take Home
Every participant leaves with five tangible deliverables — not just notes.
During the Workshop
- ·Completed lab workbook with your own command outputs and findings
- ·Extracted IOC list from the NoowaPay phishing campaign
- ·One-page AI attack chain reconstruction with MITRE ATT&CK mapping
- ·NIST CSF gap analysis — your organisation's controls mapped to each function
After the Workshop
- ✓CyBe Global Certificate of Completion — digitally signed, PDF
- ✓3 CPE credit letter — ready for submission to your certifying body
- ✓72-hour lab access — re-run any lab step at your own pace
- ✓Access to the CyBe Alumni WhatsApp community for peer discussion
The Enterprise Tool Stack
Master the exact tools enterprise SOC teams use globally -- inside real lab environments.
Detection & SIEM


Cloud Security


Endpoint & Forensics


Threat Intelligence

Scripting & Automation


AI & Adversarial AI
New

Learn to use AI as a co-analyst, investigate prompt injection and deepfake attacks, and understand how adversarial AI tools like WormGPT are weaponised against enterprise targets.
Investment & Format
Your Facilitator
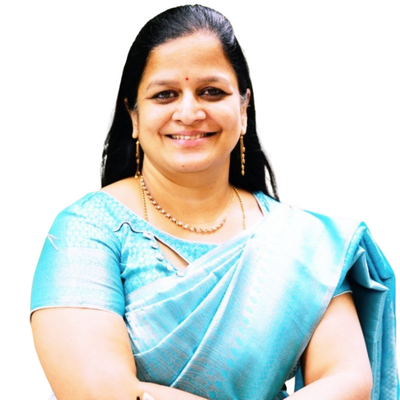
Satya
Founder, CyBe Global · Founder, CSA Bangalore Chapter
Satya brings a practitioner's perspective shaped by years of SOC operations and CISO-level advisory work. As founder of the CSA Bangalore Chapter — India's largest cloud security community with over 12,000 members — Satya has trained, advised, and convened the senior security community across India.
- ·SOC practitioner background — detection, triage, and incident response
- ·CISO advisory experience across fintech, enterprise, and regulated sectors
- ·Active community leader: null, OWASP, ISC2, ISACA, CSA partnerships
What Makes This Workshop Different
Most workshops on AI and cybersecurity are vendor-positioned slide decks with no hands-on component. This workshop was built the other way around — starting with the log data and the attack evidence, then designing the teaching around what analysts actually need to do with it.
Frameworks Referenced
- ·MITRE ATT&CK for Cloud — technique mapping
- ·NIST Cybersecurity Framework (CSF 1.1) — gap classification
- ·CSA Cloud Controls Matrix — cloud-specific controls
- ·DPDP Act 2023 — India breach notification obligations
- ·CERT-In Cyber Security Incident Reporting Framework
| # | Name | Score | XP | Badges | Speed |
|---|---|---|---|---|---|
| 1 | |||||
| 2 | |||||
| 3 | |||||
| 4 | |||||
| 5 | |||||
Sign in to see where you rank
Join thousands of cyber defenders
Ready to Register?
Seats are capped at 20 for in-person and 25 for virtual. Cohorts fill quickly. Early registration is recommended to secure the opening offer rate.
Register Now →Questions? Email support@cybe.global
Want the full 40-chapter programme?
The workshop covers the AI threat arc. The AISA: AI SOC Analyst course covers the complete NoowaPay Silent Phantom breach from first SSH probe to regulatory disclosure -- 47 lessons, around 52 hours of hands-on labs, and a recognised L1 certification.