Real labs. Verified skills.
No fluff.
63 incident reports. 174 MITRE ATT&CK techniques. One 33-day breach you investigated yourself -- inside a live Bengaluru fintech under attack.
Backed by 18 active cybersecurity leaders from Wipro, Morgan Stanley, EY GDS, Bosch, Honeywell and more.
# Day 16 -- DCSync detected in Sentinel
$ kql query --workspace noowapay-sentinel
SecurityEvent | where EventID == 4662
⚡ DCSync from NOOWAPAY-WKS12 at 03:41 UTC
$ python3 check_ioc.py --ip 185.220.101.47
⚠ Tor exit node -- ThreatFox confidence: 92%
$ soar trigger-playbook isolate-endpoint
→ NOOWAPAY-WKS12 isolated. P1 ticket created.
Step 4 of 7 -- AD Credential Attack Forensics · M2
Every lesson has two AI hooks.
How attackers use AI. How analysts fight back.
This isn't an "AI module" bolted onto the end. Every lesson in the programme shows exactly how Silent Phantom weaponised AI in that specific attack phase -- and how a modern analyst uses AI tools to detect and respond.
The phishing email was AI-written - perfect grammar, personalised from LinkedIn, no known signatures.
Use Claude to identify AI-generated phishing patterns and draft the escalation report.
AI-obfuscated process names with randomised suffixes defeated all signature-based detection.
Use Copilot for Security to summarise 847 Sysmon events and surface the three anomalies.
Kerberoasting spaced by AI-timer to stay below Sentinel analytics rule thresholds.
Use Claude to draft KQL detection rules for AI-timed credential attacks.
3 Parallel JupyterLab AI Modules
Running alongside the core investigation
AI-Assisted Log Analysis
Feed 380K-line auth.log to an LLM, validate its output, and find the hallucinated IOC before it enters the ticket.
Agentic AI Triage
Review 180 AI-pre-triaged alerts, find 3 true positives the model missed, correct 3 errors in an AI-generated runbook.
AI-Powered Detection Engineering
Draft KQL rules for Notion-based C2 with LLM assistance, map ATT&CK gaps, generate hunt hypotheses.
You join NoowaPay Technologies on Day 0.
The breach is already in progress.
Every lesson across all three paths is set inside a Bengaluru fintech processing Rs 14 crore in daily payments. This isn't a simulation. It's a 33-day breach you investigate from the inside -- building every portfolio artifact along the way.
Analyst onboarding. SOC mission. Before any alert fires.
Learn the NoowaPay stack, set up your workspace, understand the threat landscape.
nova-web-01 flagged. SSH noise. Unusual process activity overnight.
Triage the first SSH anomaly. Run Linux CLI forensics. Write your first incident ticket.
Phishing email. Four clicks. C2 beacon from NOOWAPAY-WKS12. 23 queued alerts.
Analyse AI-written phishing headers. Trace the C2 beacon. Isolate the endpoint.
Sentinel workspace opens. DC reached. secretsdump. Maldoc found.
Write KQL rules in Microsoft Sentinel. Detect DCSync. Reverse the maldoc macro.
AI-era evolution: LLM prompt injection, AI phishing, UEBA bypass, ML poisoning.
Detect deepfakes, prompt injection, and AI-generated evasion patterns using MITRE ATLAS.
AWS AdminRole assumed. S3 exfiltrated. Lambda backdoor. Azure lateral movement.
Hunt CloudTrail, revoke IAM keys, trace the Lambda backdoor, write the CISO brief.
Every chapter = one module. Every module = portfolio artifacts you keep. 33 days. 63 reports. One coherent investigation.
99 technique mappings. 14 tactics.
The only Indian programme covering MITRE ATLAS AI framework.
Every lesson is tagged to ATT&CK techniques. Students track their personal coverage map as they complete labs. Graduates can show a hiring manager exactly which techniques they have hands-on experience detecting.
The only Indian programme covering MITRE ATLAS AI framework
ATLAS maps AI-specific attack techniques -- prompt injection, model poisoning, deepfake lures, LLM jailbreaking, supply chain attacks on AI models.
Certification Alignment
Real labs. Verified skills.
No fluff.
Every lesson and micro project produces a professionally formatted incident report the student downloads, completes, and uploads back to the platform - building a coherent body of work from Day 1 SSH triage to Day 33 cloud infrastructure takeover.
Not a certificate. An actual body of work a recruiter can open, read, and evaluate.
Start free. Go deep. Graduate credentialed.
Every path starts free with no prerequisites. Assessments gate each level, so you always know exactly where you stand.
Discover
Free assessment maps your skills to a career path.
02⚡Spark
CS1 Cyber Spark: free, browser-only foundations.
03🛡️Choose your path
10 career paths. Baseline, then go deep.
04🏆Go pro
SA1/SA2 full analyst programme + the Siege.
SOC Analyst Foundations
The highest-demand entry-level cyber role in India. Triage, KQL, Microsoft Sentinel and live terminal labs -- then sit the CP1 exam to unlock the full SA1 analyst programme.
The Enterprise Tool Stack
Master the exact tools enterprise SOC teams use globally -- inside real lab environments.
Detection & SIEM


Cloud Security


Endpoint & Forensics


Threat Intelligence

Scripting & Automation


AI & Adversarial AI
New

Learn to use AI as a co-analyst, investigate prompt injection and deepfake attacks, and understand how adversarial AI tools like WormGPT are weaponised against enterprise targets.
72 hours. All attack vectors live.
Pass/fail. CISO panel.
No participation grade. No hand-holding. Every decision you make must be documented in a written audit trail the CISO panel reads.
First Contact
Endpoint C2 active. LLM being interrogated. AWS AssumeRole confirmed.
Triage all three vectors in 45 minutes.
Containment Race
NOOWAPAY-DC01 isolated. NOOWAPAY-SRV07 still live. Supply chain package pulled by three payment instances.
You have hours before the attacker pivots.
The Phantom Resurfaces
Containment appeared complete. New alert: LLM queried by a session matching attacker fingerprint.
Find the gap. Close it before hour 72.
Final Debrief
Attacker out. CISO waiting. Your report determines what gets disclosed to regulators.
Pass/fail. Graded by CISO panel. No participation grade.
The SOC Siege Certificate
The highest credential CyBe offers. Rare. Earned. When a graduate tells a hiring manager "I passed a 72-hour live breach response graded by active CISOs" -- that conversation goes differently.
Learn about SOC Siege →Built with 18 active cybersecurity leaders
From Wipro, Morgan Stanley, EY GDS, Bosch, Honeywell, TCS, Saviynt, and Volvo. These are the practitioners who set security standards for India's enterprise sector -- and the kinds of teams your graduates will be stepping into.
Abhinay Adiraju
Director – Information Security
Saviynt
Amod Suresh Puranik
Director – Head Data & AI Security
Virtusa Corp
Ashish Shrivastava
Director – Cyber Security
Honeywell
Ashwini Siddhi
Co-Founder & CEO
Securacy.AI
.jpg)
Babji VS
Strategic Advisor & Consultant – UAE & Middle East
Ahana Systems & Solutions
Dr. Abhilasha Rakesh Vyas
Director, Learning & Innovation
PureID
Dr Ram Kumar G
Cyber Security and Risk Leader
Volvo Group
Madhukeshwar Bhat
Academia Advisor
CSA Bangalore Chapter
Pooja Agrawalla
Co-Founder
CyBe Global / CSA Bangalore
Prabhu Pathak
Director
LogiCoy
R S Lakshminarayanan
GM & Regional CISO
Wipro Limited
Raveesh BS
Director
Aishan Technologies
Ravi Subbiah
Managing Partner
TCS Ltd
Rohit Sadgune
Senior Manager, Cyber Defence
Saviynt
Sai Lakshmi Sathyanarayana
Partner, Cyber Leader
EY GDS
Satyavathi Divadari
CEO & Founder
CyBe Global / CSA Bangalore
 (1).jpg)
Seema Khandelwal
Core Member
CSA Bangalore Chapter
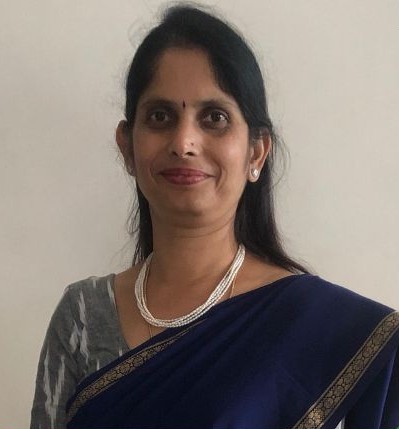
Shobha Jagathpal
Managing Director
Morgan Stanley
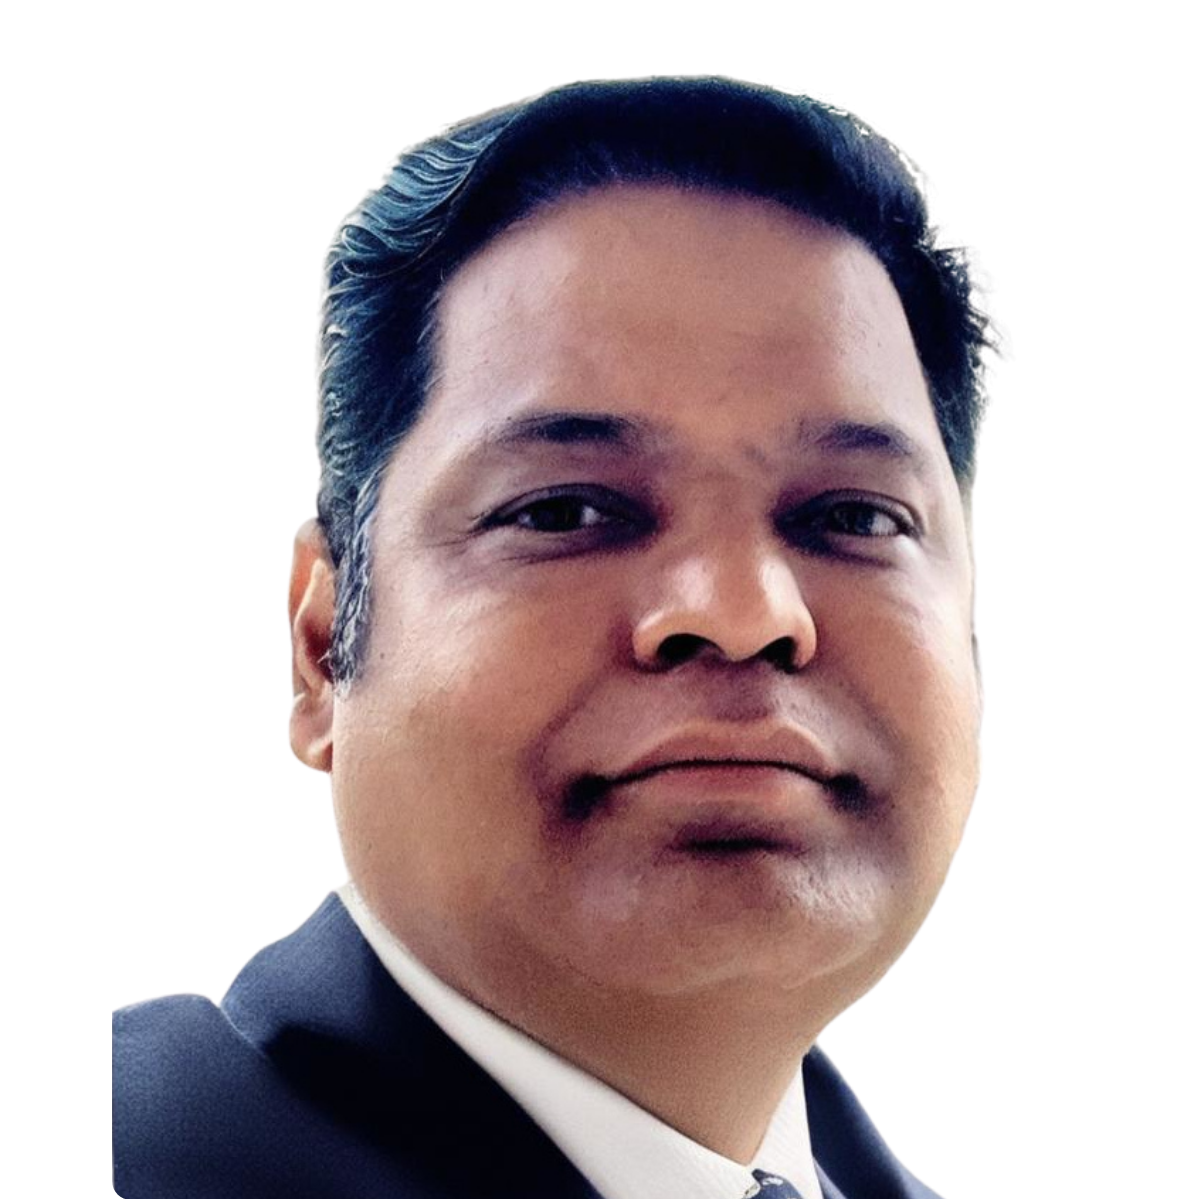
Vishal Saraswat
Head, Research & Innovation, Cybersecurity
Bosch Software
Bridging Campus to Career
Partner colleges integrate CyBe Global into their curriculum -- VTU SEC credit, internship hours, and verified certification before graduation.
Madras Engineering College
Chennai, Tamil Nadu
✓ Active PartnerExpanding Across India
Where Our Graduates Go
Companies that hire directly from the CyBe Global talent pool -- no cold applications, no resume black holes.
How placement works
On graduation, you get warm introductions to 3-5 hiring partners appropriate to your location and specialisation -- through the CSA Bangalore Chapter network, not a cold jobs board. Partners receive your public portfolio link alongside your certificate.
Across India's Campuses
CyBe Global has collaborated with engineering colleges, law schools, and universities across India to bring cybersecurity awareness to students.
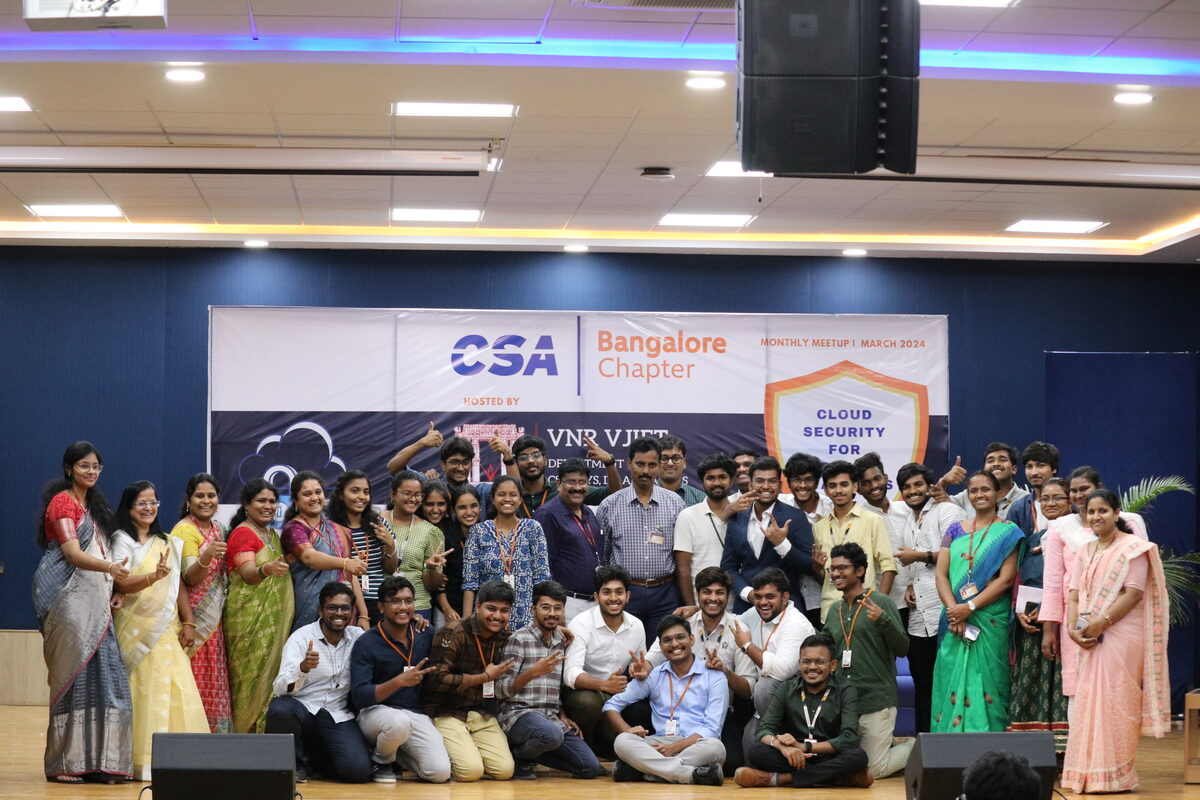
VNR VJIET, Hyderabad
CSA Bangalore Chapter · Cloud Security Workshop · March 2024
Regional News Coverage
Telangana -- Eenadu, Sakshi, Vaartha, Surya · March 2024
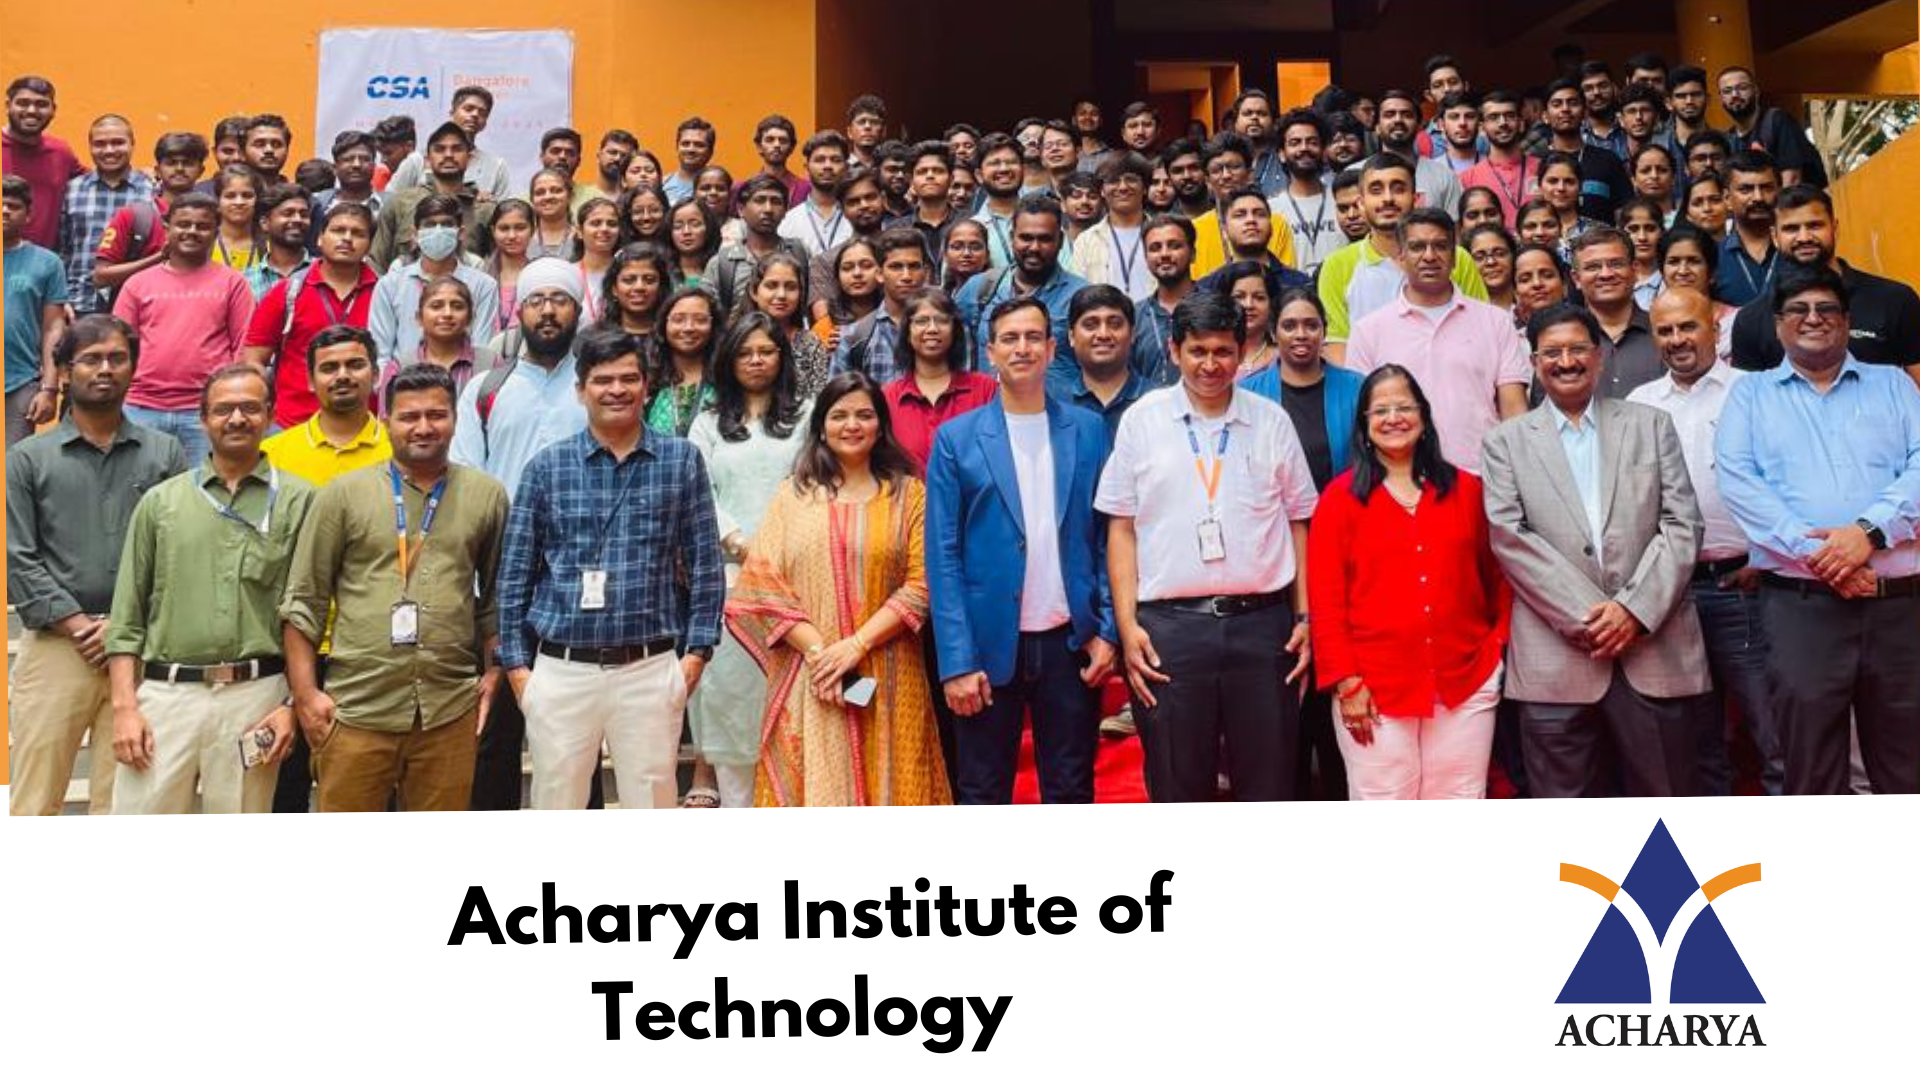
Acharya Institute of Technology
Bangalore · CSA Bangalore Chapter Meetup
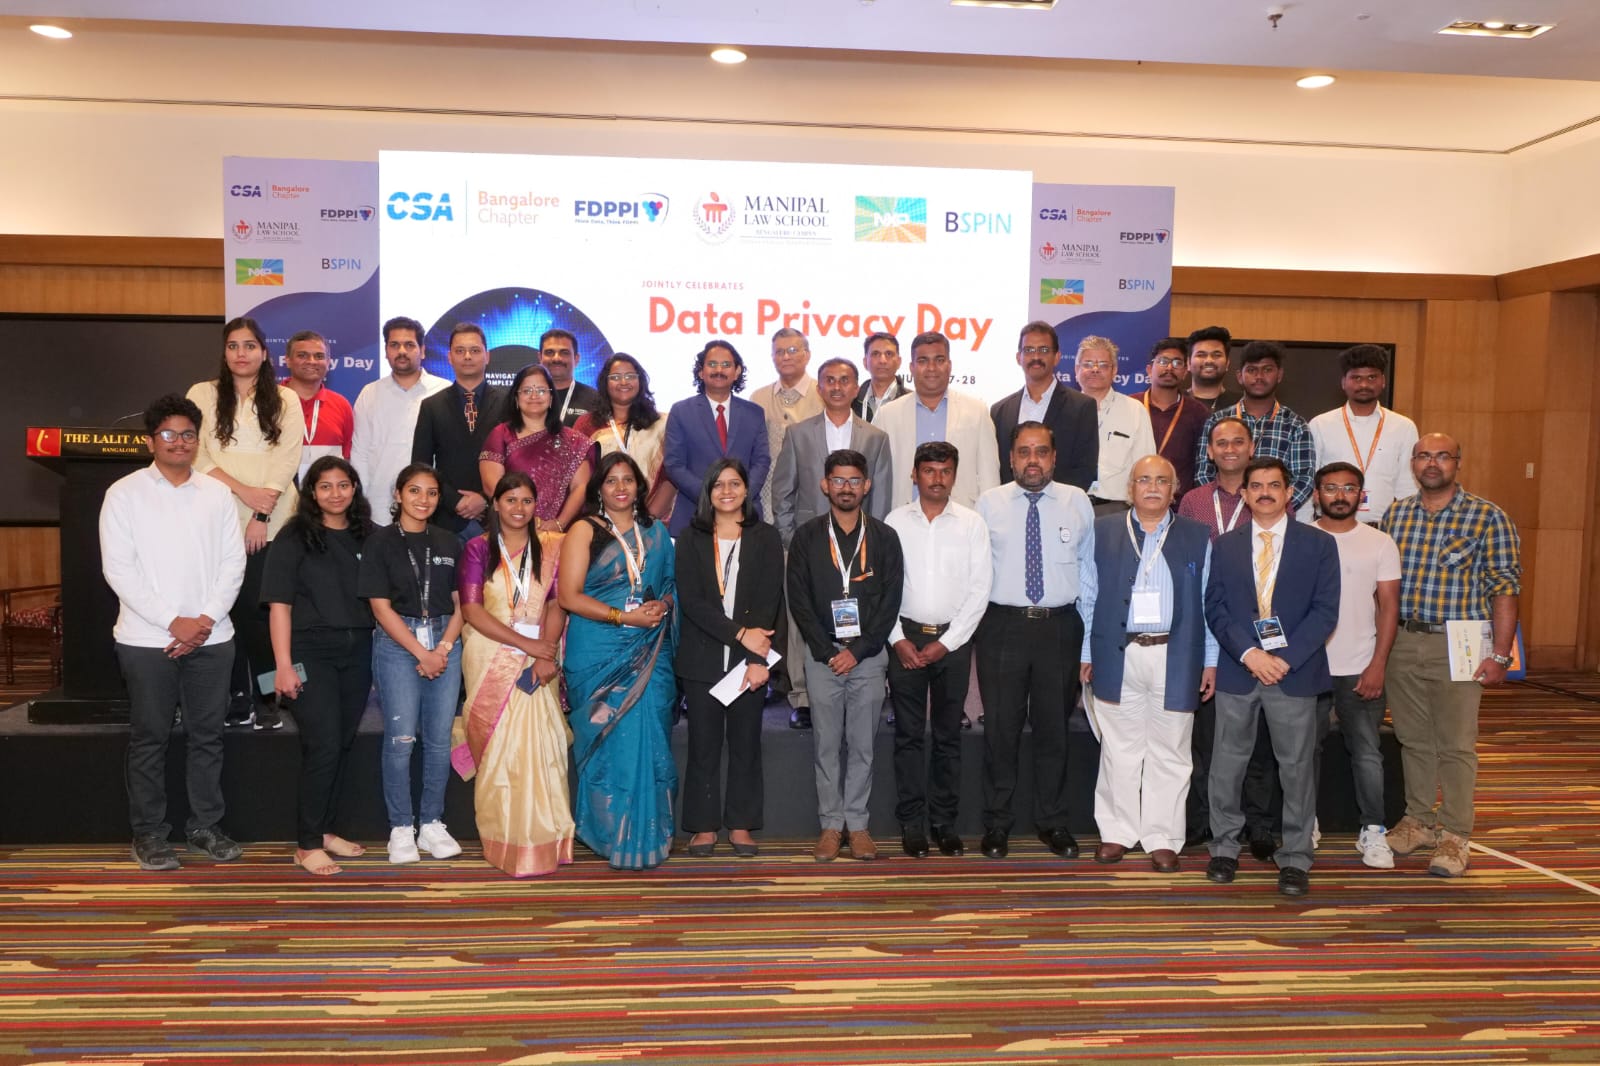
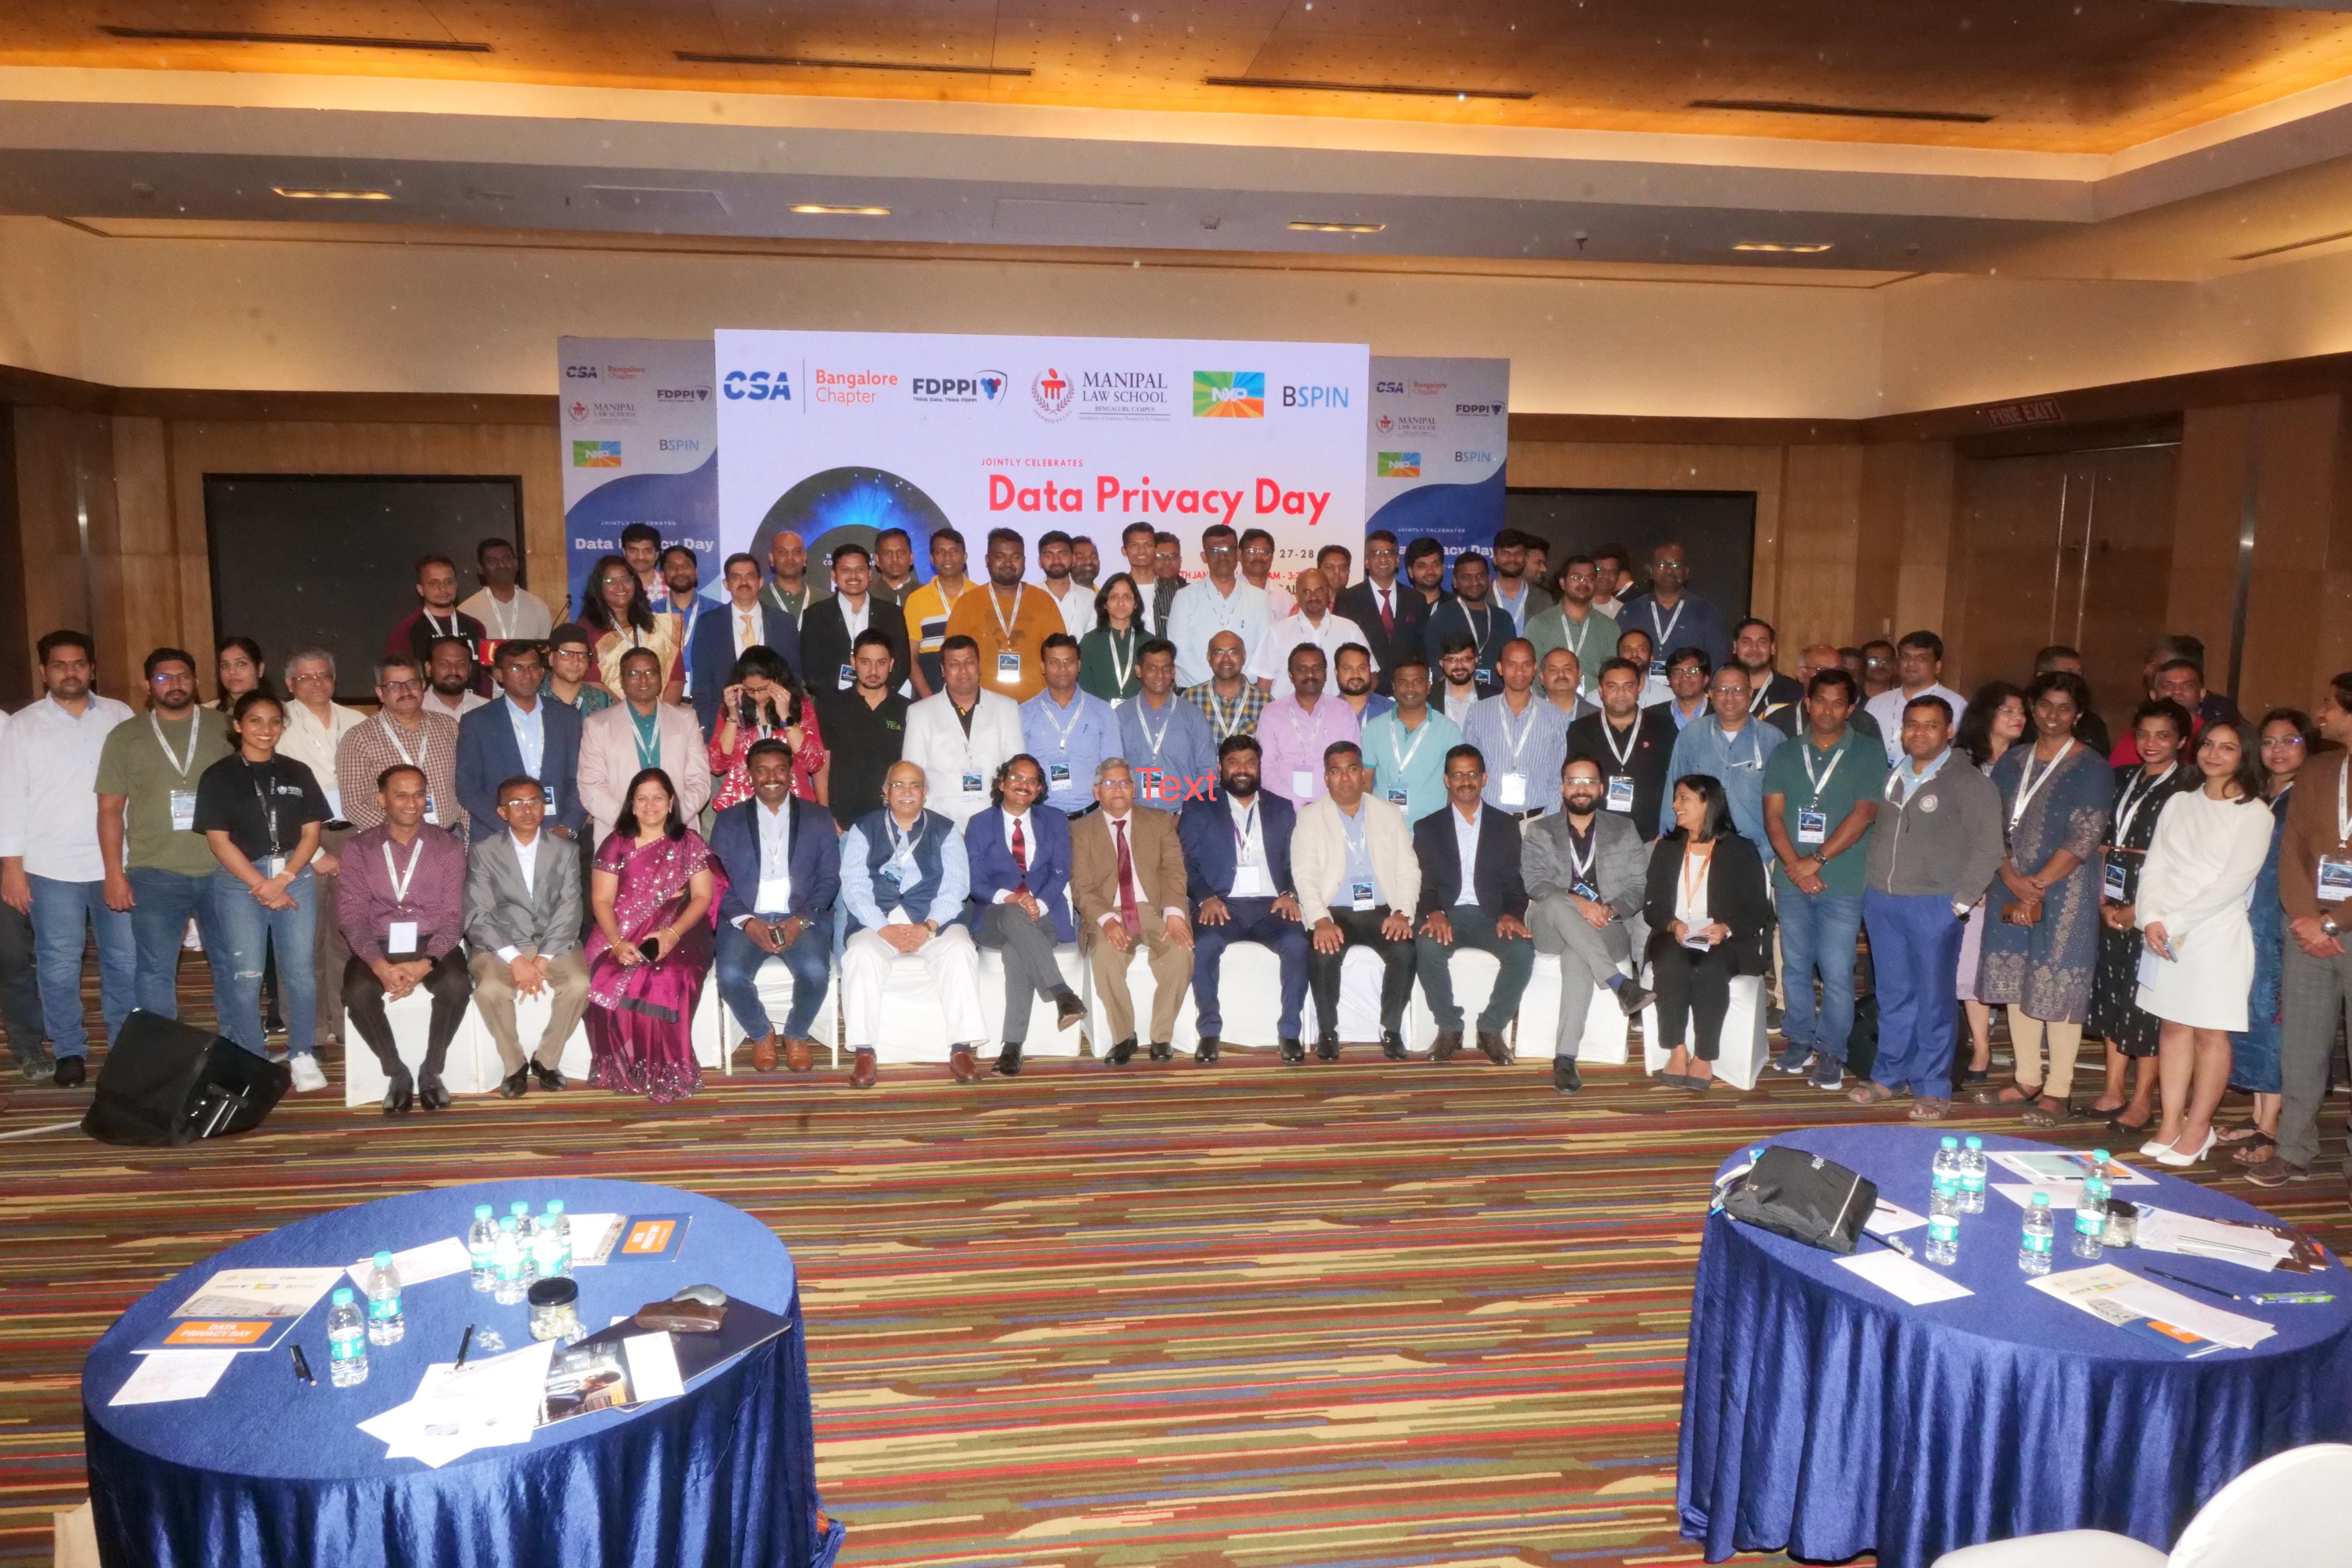
Manipal Law School, Bengaluru
Data Privacy Day · Jointly with CSA Bangalore, FDPPI, BSPIN
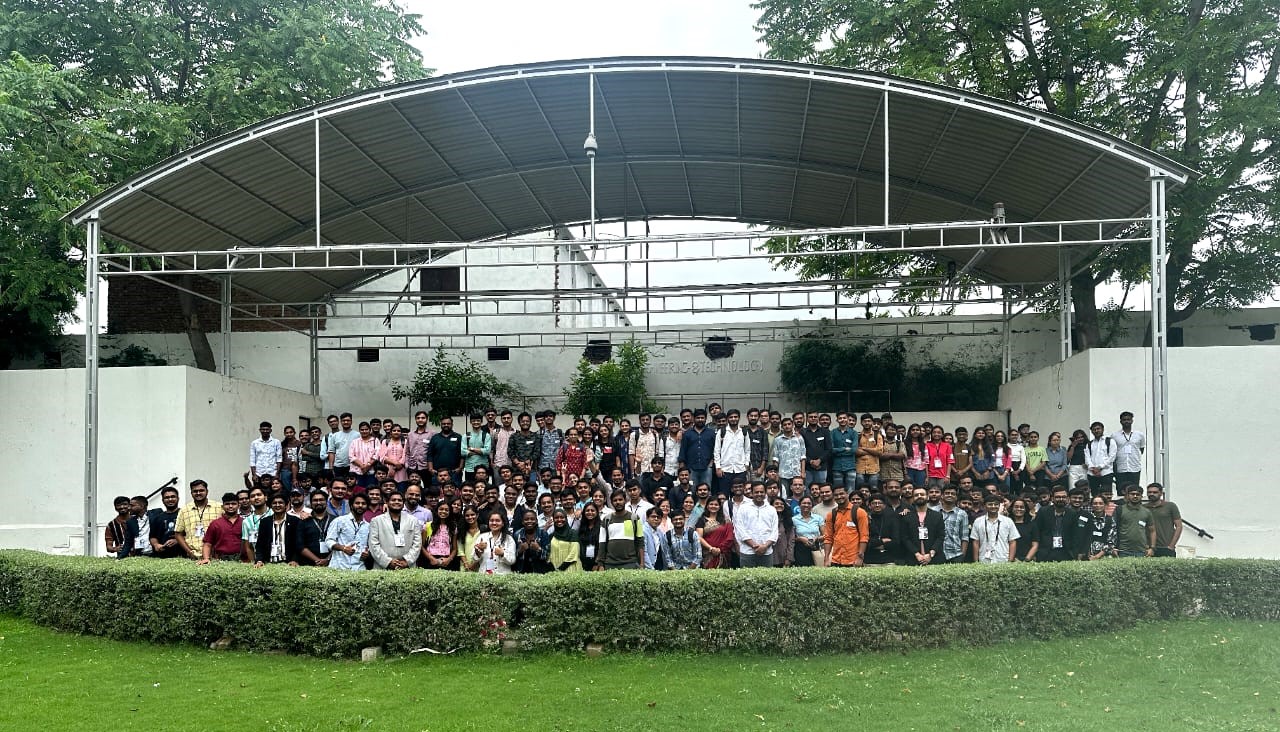
LJ University, Ahmedabad
Cloud Security Awareness Workshop
Workshops & Micro Projects
Focused skill sprints and real breach scenarios. Start anytime. No cohort required.
CyBe Global builds India's most industry-connected cybersecurity career platform — where every lab runs on real enterprise tooling and every credential is backed by practitioners, not just instructors.
Founded by the leadership of CSA Bangalore Chapter, CyBe Global was built to close the gap between classroom cybersecurity and what India's enterprise SOCs actually need. Our curriculum is designed with and reviewed by active CISOs. Our labs replicate real incidents — not textbook scenarios. Every graduate is connected directly to our hiring partner network.
Learn more about CyBe →CSA Bangalore Chapter
Cloud Security Alliance
- ✓CSA Bangalore Chapter — Founding Member Organisation
- ✓Cloud Security Alliance Global Recognition 2024
- ✓Industry Practitioner-Led Curriculum — CSA Endorsed
- ✓18 active CISO advisors from India's leading enterprises
Our CISO faculty are drawn from the CSA Bangalore network -- practitioners who set security standards for India's enterprise sector.